Cybersecurity Resources

- BlogCMMC Phase 2 pause: Why CMMC compliance work should continueCMMC Phase 2 is paused, but that doesn't mean organizations should stop preparing. The standards behind CMMC remain relevant, and organizations that continue investing in readiness will be better positioned for whatever comes next.
- BlogWhen Device Data Disappears: 4 Endpoint Backup Gaps for MSPsCybersecurity GlossaryData SecuritySaaS Backup
- BlogAI at work: Frontier transformation for MSPsKeelin Conant shares practical takeaways from OpenMic podcast Episode 1 on turning AI ambition into secure, measurable business value.Data ProtectionData Security
- BlogAI Security Assessment for secure AI adoptionLearn how an AI Security Assessment helps SMB and mid-market organizations identify AI risks, strengthen governance and adopt AI securely.Data ProtectionData Security
- BlogWhy MSP security stack complexity limits growthHow to reduce operational drag, protect margin, and create capacity for recurring servicesMicrosoftSecure Cloud
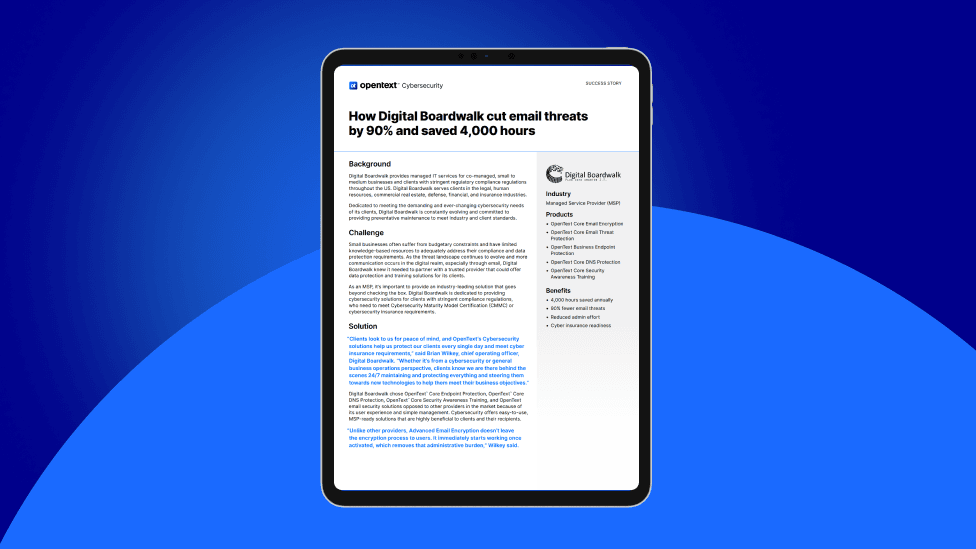
- Case StudyDigital Boardwalk cuts email threats by 90% and saves 4,000 hours annually with OpenText CybersecurityDigital Boardwalk standardized on OpenText Cybersecurity solutions to strengthen client protection, reduce cyber risk, and simplify security management across its customer base.CyberthreatsEmail Security
- BlogMicrosoft CSP change: What it means for MSP margin strategyLook beyond headline license margin to understand the full value of your Microsoft business model.MicrosoftSecure Cloud
- Blog7 steps to build a disaster recovery planHow to create a disaster recovery plan that keeps your business operating when critical systems become unavailableData ProtectionData RecoveryData Security