OpenText Managed Detection and Response (MDR)
Solution snapshot

Get built-in SIEM and SOAR included natively, not paid add-ons or upgrades

Detect attacks that never touch the endpoint, from identity to cloud

Contain threats with SOC-led response, with consent controls for high-impact actions

Extend MDR coverage with an extensive set of syslog and API integrations

Receive investigated incidents, not raw alerts, from 24x7x365 expert analysts

Layer flexible coverage onto your existing stack without replacing current tools
Why managed detection and response matters
Security talent is scarce, and AI-assisted cyberattacks are becoming faster and more sophisticated. Most organizations struggle to build a full security team and stay ahead of evolving threats.
OpenText MDR bridges this gap with enterprise-grade detection technology and an always-on security operations center (SOC). We monitor across endpoint, identity, email, network, and cloud, investigate suspicious activity, and take targeted response actions so your business stays protected around the clock. You have visibility into every alert and action we take, while retaining control over decisions that could disrupt your business.
Customized service options
OpenText MDR offers powerful security oversight that enhances your posture. Our MDR service combines automation, expert analysts, and extensive integrations to provide 24x7x365 threat monitoring, investigation and targeted response without the cost and complexity of building in-house capabilities.
For organizations that want a service tailored to their environment, we offer flexible options, from digital forensics and incident response support to a more fully managed service with a dedicated point of contact. To find out more, please contact us
Benefits of MDR for your business

Enhanced security posture
Identify and contain threats faster with continuous monitoring by experienced security analysts.

Extend security expertise
Gain access to expert SOC analysts without the overhead of recruiting and maintaining internal security staff.

Reduce alert fatigue
Our analysts investigate and validate alerts within your covered categories, so your team deals only with prioritized, actionable incidents.

Accelerate containment
The SOC takes direct action on validated threats, while consent settings keep you in control of higher-impact response actions.

Gain broad visibility
Uncover hidden risks across your IT ecosystem, such as network and indicator-of-compromise (IOC) threats, data exfiltration risks, and risky browser extensions.

Simplify cyber compliance
Support cyber insurance and regulatory requirements with round-the-clock monitoring, detailed audit trails, and customizable reports.
MDR features working for you, 24×7×365
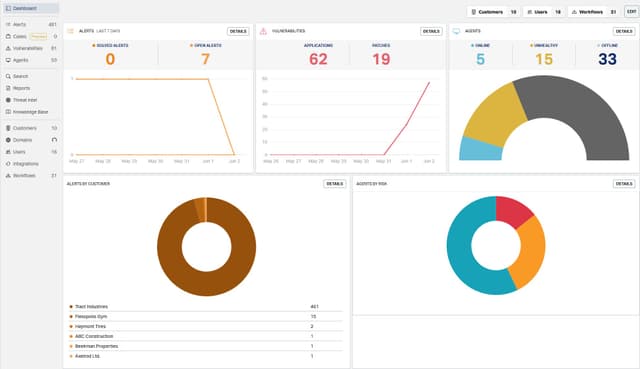
Intercept stealthy attack vectors at initial access, stop lateral movement, and neutralize risks. Our MDR service delivers broad threat detection with visibility and operational control that stays with you

End-to-end data inspection
Continuously monitor system logs, network activity, identity events, and risky or untrusted browser extensions to expose hidden entry points

Identity and access defense
Detect unauthorized access, credential misuse, and suspicious login behaviors using targeted identity and access attack detection

Correlated detection across sources
Built-in SIEM correlates endpoint, identity, email, network, and cloud telemetry to surface threats that single-source tools miss

Exfiltration risk detection
Receive data exfiltration risk alerts when sensitive files or confidential corporate data are targeted for unauthorized removal

Extensive ecosystem integrations
Receive always-on monitoring and advanced threat detection across your environment by integrating with your security stack

Collaborative response workflows
Consent settings let you authorize higher-impact actions in advance, so containment doesn’t wait, and anything outside them comes to you with context and a recommendation.
How managed detection and response works
Telemetry from the tools you already run flows into the OpenText Detection & Response platform, where built-in SIEM and SOAR correlate activity across endpoint, identity, email, network, and cloud.
Our SOC investigates what matters, filters out the noise, and takes targeted response actions on validated threats. For higher-impact actions, your consent settings determine whether our SOC can act immediately or provide context and a recommendation, keeping you in control of how threats are handled.
Why customers choose MDR to stay resilient
Endpoint protection builds the trust. MDR builds the resilience. With OpenText Cybersecurity, it’s a natural evolution from protection to active threat response.
Resources

24x7x365 co-managed detection and response that helps organizations expand security monitoring, investigation, and initial response without staffing a full, in-house SOC.
Learn how one leading MSP elevates customer security from basic protection to active 24/7 threat response using OpenText MDR.

Find out how MDR combines technology with human expertise to rapidly identify new and emerging threats.
FAQs
No. OpenText MDR works alongside a broad range of existing security tools, so you can keep supported products rather than replacing your security stack. More than 35 built-in API integrations are included in your subscription. Syslog ingestion from hundreds of additional sources, such as firewalls, switches and servers, is available through the Compliance Storage add-on, billed on the volume of data stored over your chosen retention period.
The SOC takes non-disruptive actions on its own where your integrations support them, such as quarantining a file, running a scan, or revoking an active session. For higher-impact actions, such as isolating an endpoint or disabling an account, your consent settings determine whether the SOC can act immediately or escalate to you with context and a recommendation, keeping you in control of decisions that affect your business.